How Book & Sharing Work
ChangelogJustwrite is built for privacy. We use accountless end-to-end encryption so your notes stay private on your own devices.
1. Zero-Knowledge Privacy
You don't need an email or account to write. Your notes are encrypted inside your browser before leaving your phone or computer. The server only stores scrambled data and cannot read your writing.
2. “Your Book” Sync
Your Book uses a simple 4-word code (like alpha-delta-zulu-mike) to pair your devices. Your devices derive an AES-256 encryption key locally to lock and unlock your notes.
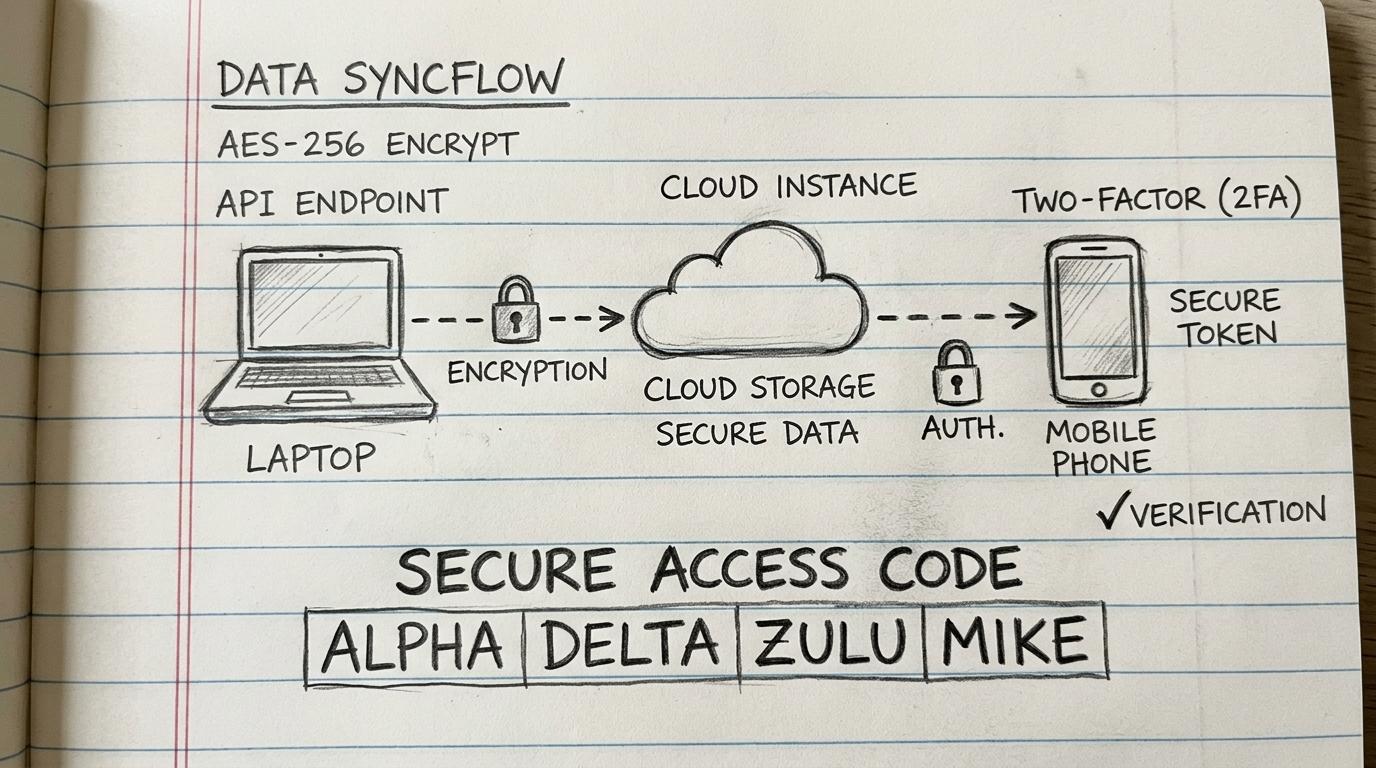
Client Encryption Code:
// 1. Generate 256-bit encryption key locally in browser
const aesKey = await crypto.subtle.deriveKey(
  { name: "PBKDF2", salt, iterations: 50000, hash: "SHA-256" },
  keyMaterial,
  { name: "AES-GCM", length: 256 },
  false,
  ["encrypt", "decrypt"]
);

// 2. Encrypt notes on your device before sending to server
const encrypted = await crypto.subtle.encrypt(
  { name: "AES-GCM", iv },
  aesKey,
  new TextEncoder().encode(noteContent)
);
3. Private Note Sharing
When you share a note, a secret key is added to the link after a # symbol (e.g. /s/note#key=123).
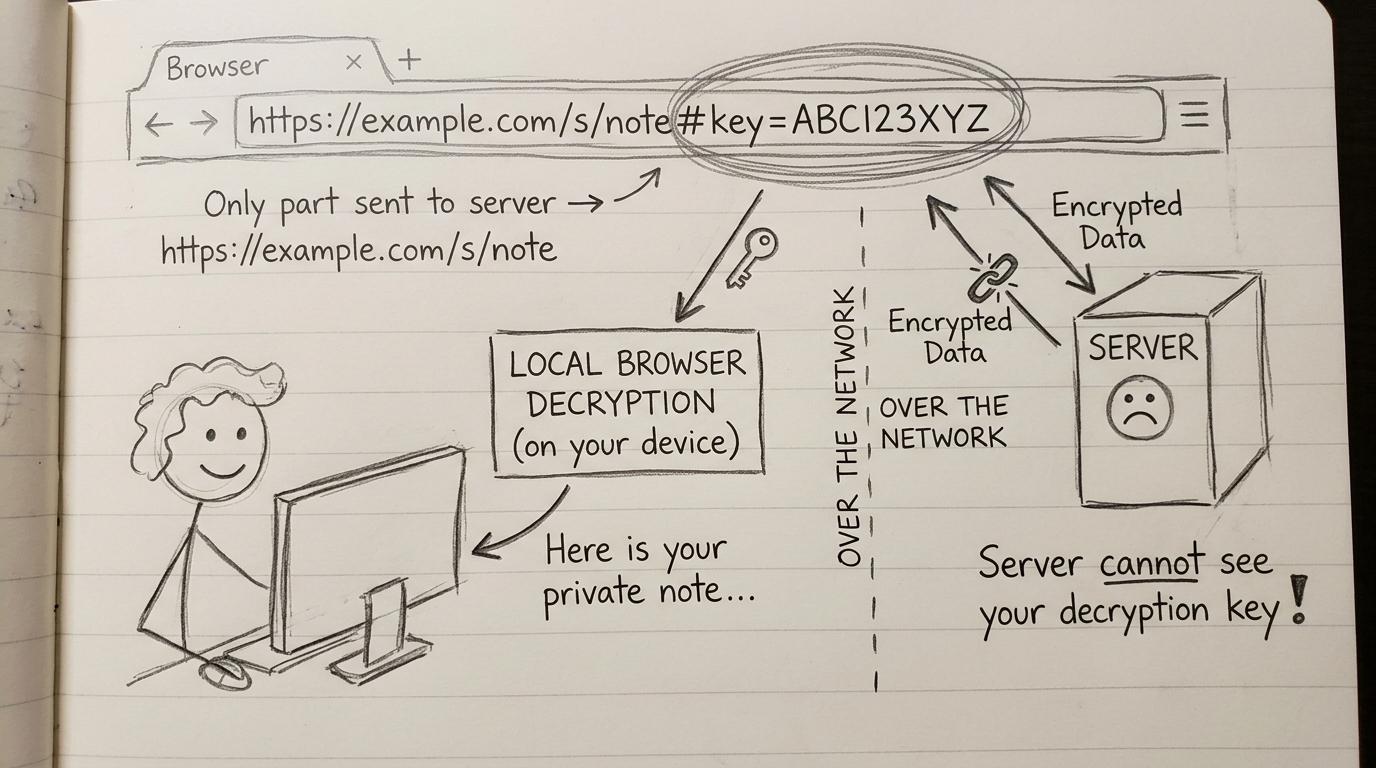
Web browsers never send the #key part to the server. The server only sees the encrypted note ID, so your secret key never leaves the link.
4. Summary
| Feature | Traditional Apps | Justwrite |
|---|---|---|
| Account | Required | None |
| Encryption | Server-side | Client-side (AES-256) |
| Secret Links | Server readable | URL hash (Browser only) |
Advertisement